 ⬇️
Key Takeaways
- Internet-exposed refrigeration controllers can give attackers a path to manipulate temperatures, defrost cycles and monitoring data
- Hospitals, food suppliers, chemical operators and transportation companies face physical, safety and financial consequences
- Federal agencies recommend reducing internet exposure, segmenting OT networks, updating equipment and testing offline backups
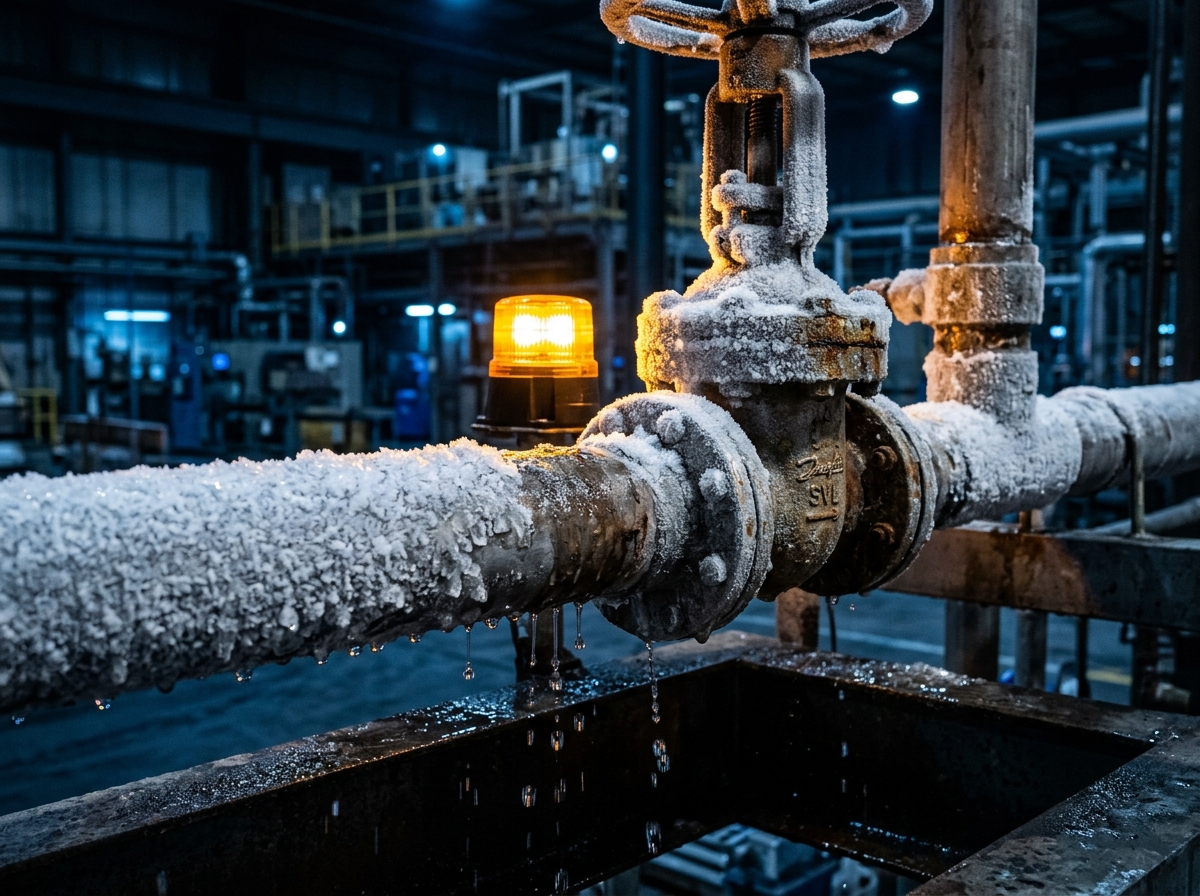
CISA, working with the FBI, HHS, USDA and DOT, has warned critical-infrastructure operators to strengthen the security of industrial refrigeration and cold-chain monitoring systems. The November 5 advisory focuses attention on equipment that often sits outside conventional enterprise security programs, despite controlling storage conditions for blood, medicines, food and temperature-sensitive chemicals.
The concern is not simply that attackers could steal operational data. Compromised refrigeration controllers could allow them to change temperature setpoints, initiate continuous defrost cycles or conceal actual temperature readings. Those actions can spoil inventory, damage compressors, create fire hazards and leave sensitive products stored outside approved conditions.
For hospitals, the stakes are particularly sharp. Blood products, vaccines, medicines and laboratory materials depend on narrow temperature ranges. If monitoring data is suppressed or falsified, staff may not immediately recognize that stored materials have become unsafe. A technically successful recovery of the controller would not restore the affected inventory or resolve uncertainty about whether it remained usable.
Refrigeration technology was not traditionally treated like a prominent cyber target. Controllers were commonly installed for reliability, energy management and remote maintenance, then left in service for years. Some are now reachable from the public internet, use weak configurations or run firmware that has not been updated. End-of-support equipment adds another complication because security fixes may no longer be available.
Federal officials identified authentication bypass, arbitrary code injection and insecure configurations as possible attack paths. The affected technologies handle temperature logging, alarms, defrost management and energy optimization across healthcare, food, chemical and transportation environments. That combination of digital access and physical control makes them attractive to disruptive attackers, including ransomware groups seeking operational leverage.
Could an attacker cause more pressure by encrypting office files or by threatening a hospital's blood supply? Increasingly, security teams have to plan for both.
The warning also reflects lessons from reported European incidents involving supermarket cooling equipment and France's national blood service. Those cases showed how interference with refrigeration can move quickly beyond an IT outage. Products may need to be discarded, facilities may lose operating capacity and organizations may face regulatory or patient-safety reviews.
The immediate response begins with visibility. Operators should identify refrigeration controllers, monitoring gateways, remote-access services and associated software, including systems built around technologies from Danfoss, Carel and Sensitech. Asset records should capture firmware versions, support status, network connections, responsible owners and the business processes each device supports.
Public-internet exposure deserves early attention. Where direct access is not operationally justified, organizations can remove it and place remote connections behind controlled gateways. Operational technology networks should also be separated from corporate IT environments, with tightly limited communication between zones. That reduces the chance that a compromised laptop, stolen account or phishing incident becomes a route into physical systems.
Identity controls matter too. Phishing-resistant multifactor authentication can help protect remote maintenance accounts, while unique credentials and role-based permissions can reduce reliance on shared administrator access. Firmware updates should be tested and deployed according to operational risk, and unsupported equipment should enter a planned replacement process rather than remaining invisible on the balance sheet.
The NIST Cybersecurity Framework 2.0 offers a useful structure for this work, particularly its emphasis on governance, asset identification, protection, detection, response and recovery. CISA's Cybersecurity Performance Goals add practical priorities such as OT segmentation, exposure reduction, patching and stronger authentication.
Backups are part of the picture, but configuration files alone are not enough. Operators should maintain tested offline copies of controller settings, monitoring-system data and recovery procedures. They also need manual temperature checks, independent alarms and clear escalation paths for situations in which digital readings cannot be trusted.
That said, the broader lesson is organizational. Refrigeration security crosses facilities, biomedical engineering, IT, cybersecurity, procurement and clinical or operational leadership. Treating it solely as a maintenance issue leaves gaps. For businesses dependent on cold storage, these controllers are production systems with direct consequences for safety, revenue and continuity.





